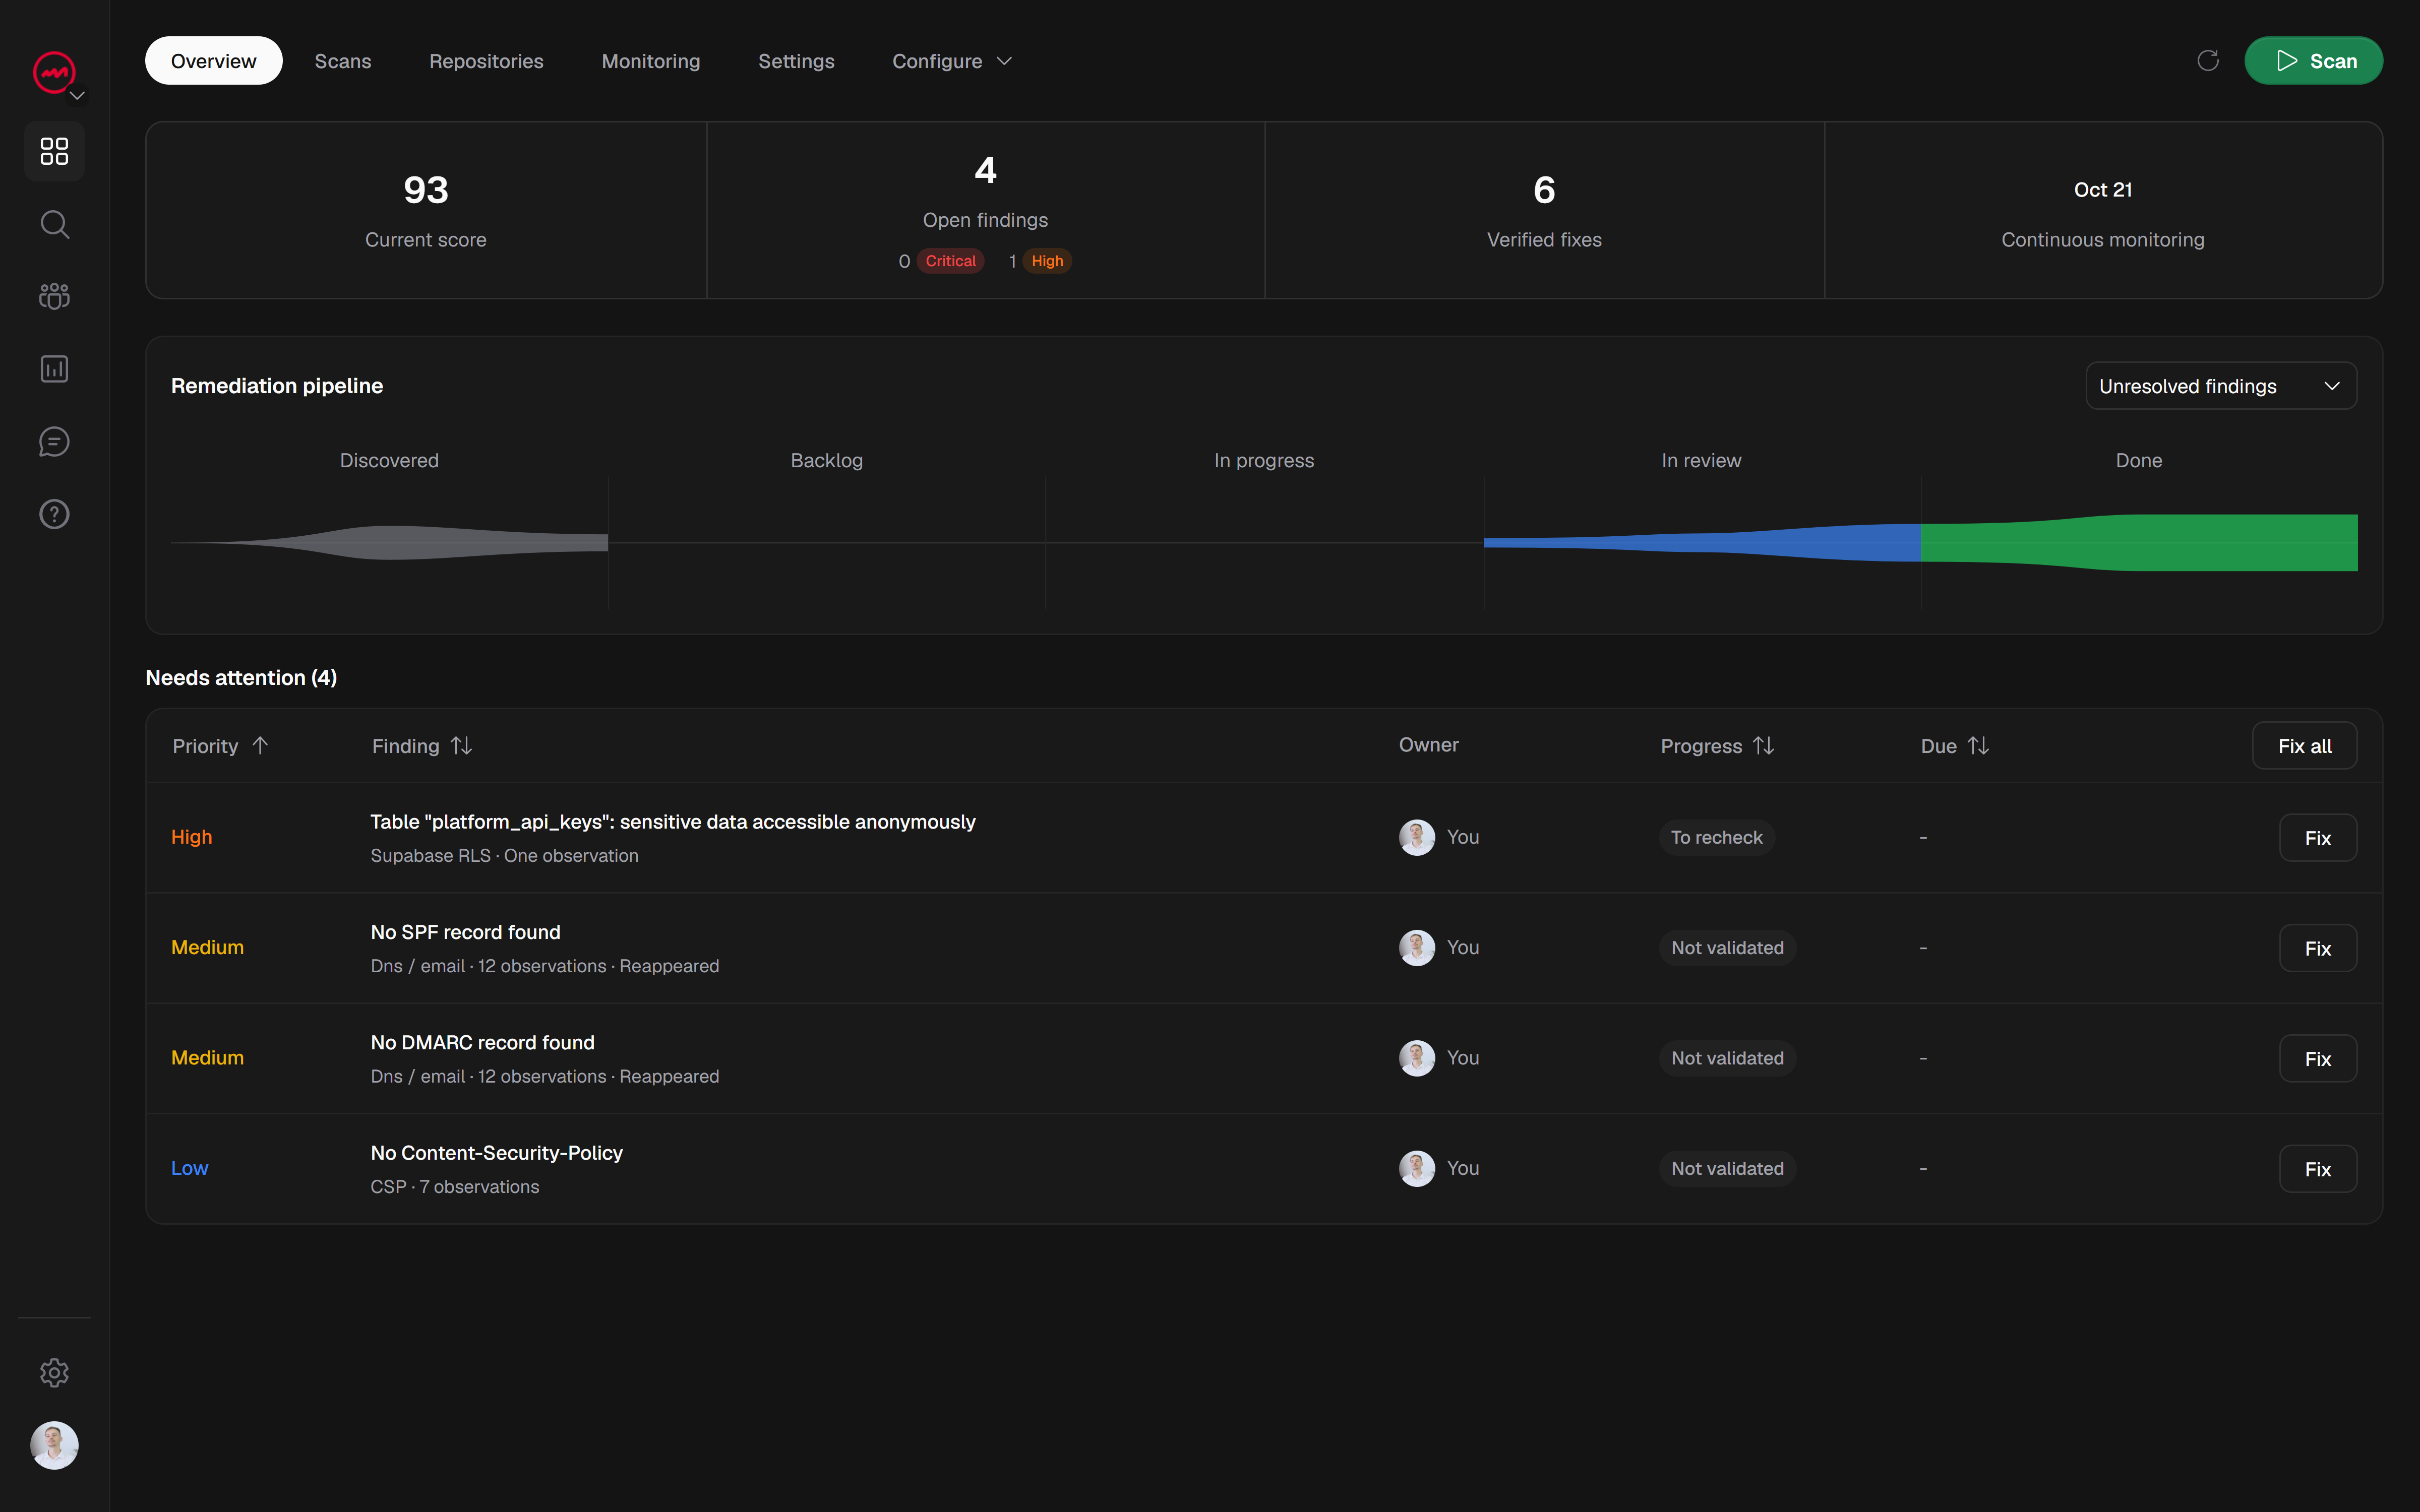
The security of your WordPress, beyond HTTPS.
Identify exposed users, sensitive entry points and your WordPress site’s public configuration, with recommendations you can act on.






Look what your WordPress shows.
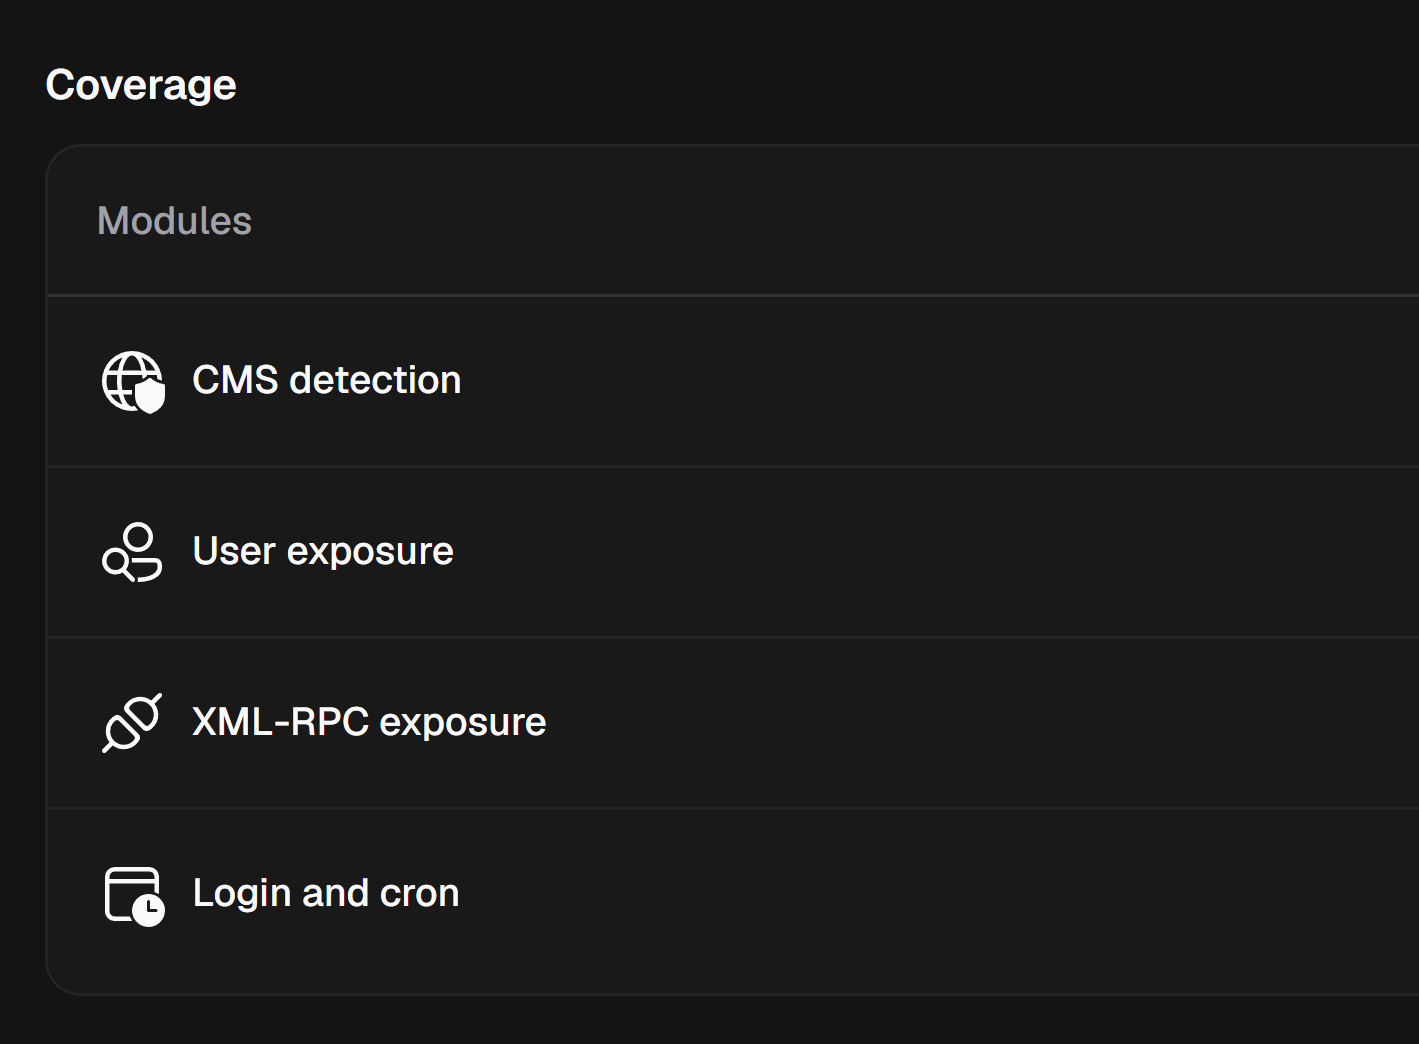
VICE first confirms that WordPress is present, then examines surfaces specific to the CMS. Track these findings alongside the rest of your site.
The security of your WordPress,
step by step.
 The authors of your site
/wp-json/wp/v2/users/?author=1Exposed users
Author pages and the REST API can reveal the usernames of accounts that publish on your site. VICE checks both paths and saves its observations to help you decide what information should remain public.
 Test request
POST /xmlrpc.php<methodCall> <methodName>…</methodName> </methodCall>
XML-RPC
Some plugins and services use XML-RPC to communicate with WordPress. VICE checks the responses of this entry point and the observable behaviors, in order to distinguish its simple presence from an exposure that deserves correction.
/wp-login.php/wp-cron.phpLogin and cron
The login page and scheduled task triggers are two different entry points. VICE examines them separately and preserves their context, helping you identify access to protect without mistaking a public route for a vulnerability.
Regular monitoring
A theme, plugin or configuration update can change what your site exposes. Plan the checks, compare the findings between two scans and rerun the relevant tests to check the corrections you have applied.
The WordPress profile requires a verified domain and a subscription or credit. Coverage depends on the surfaces detected.
Frequently asked questions
Start checking
the security of your site.
Find issues, prepare fixes and verify changes.
Keep your results together for the next deployment.